10 min
10 AWS Cloud Security Best Practices: An Implementation Guide for 2026
Most AWS security breaches come from misconfiguration, not AWS failures. Here are 10 concrete best practices to harden your AWS environment in 2026.
 Nash Ogden

Blog category
Most AWS security breaches come from misconfiguration, not AWS failures. Here are 10 concrete best practices to harden your AWS environment in 2026.
Nash OgdenProduction guide for HIPAA-compliant generative AI on AWS Bedrock: BAA scope, eligible models, Guardrails for PHI redaction, Knowledge Bases for RAG over clinical data, VPC isolation, and the audit evidence package OCR investigators expect.
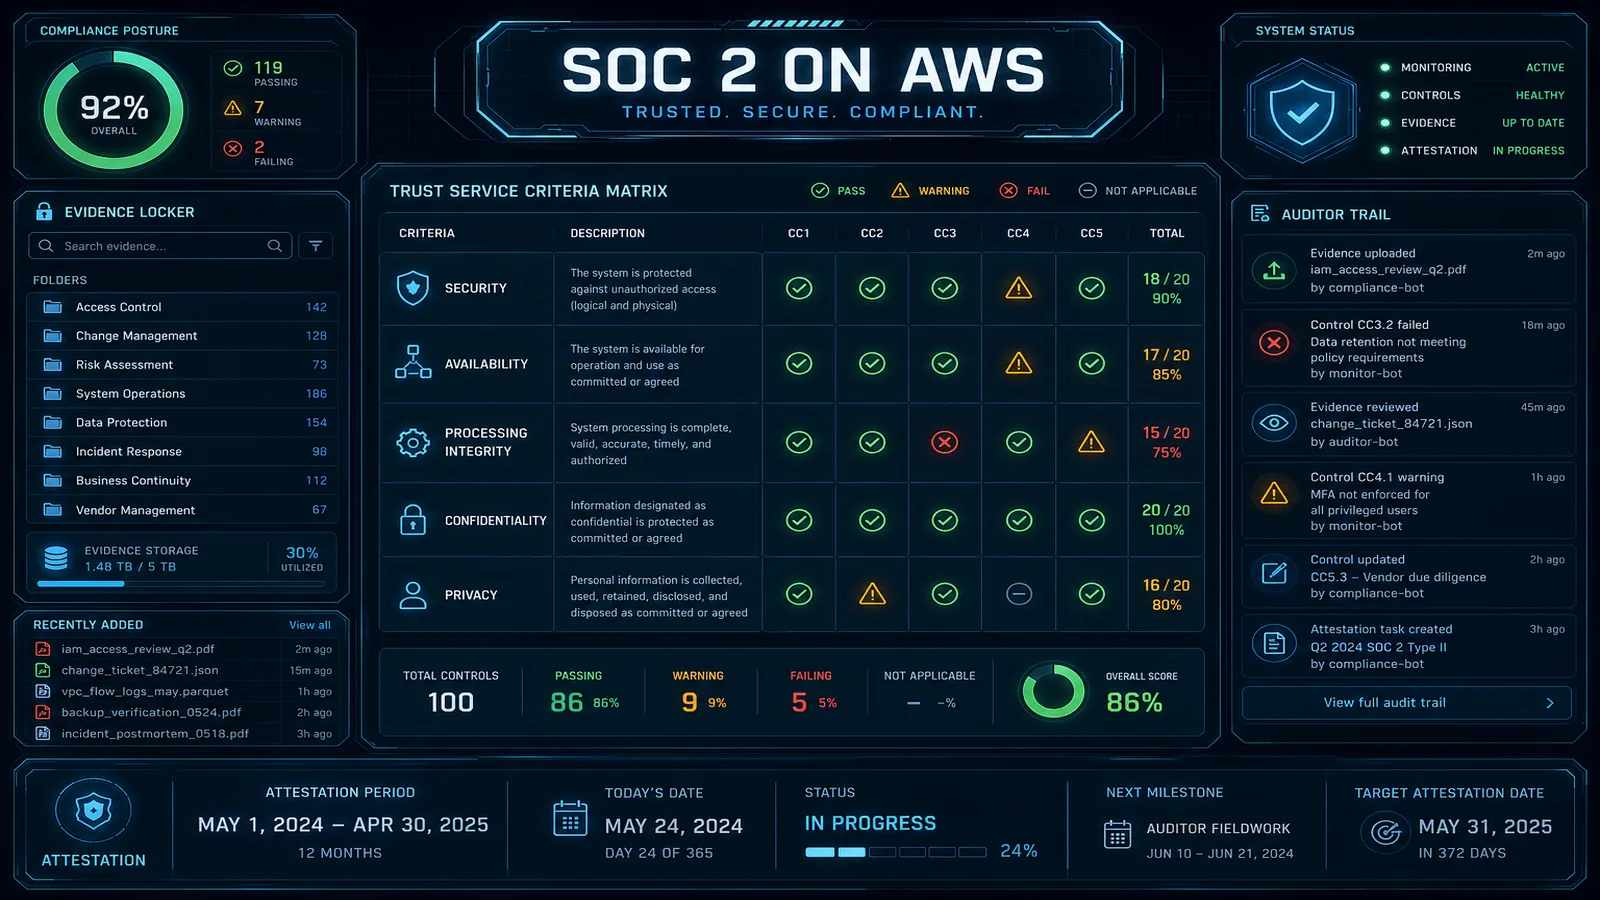
Nash OgdenSOC 2 Type II certification proves your controls are effective over 6-12 months. This guide covers the compliance roadmap, AWS security controls, documentation requirements, and audit preparation for 2026 certification.
Nash OgdenWAF beyond “enable managed rules”: COUNT→BLOCK, rate limits, Bot Control cost traps, GraphQL depth. July 2026 API protection checklist.
Nash OgdenHIPAA on AWS build guide: BAA via Artifact, eligible services, KMS/VPC/RDS/S3 patterns. July 2026 engineering checklist.
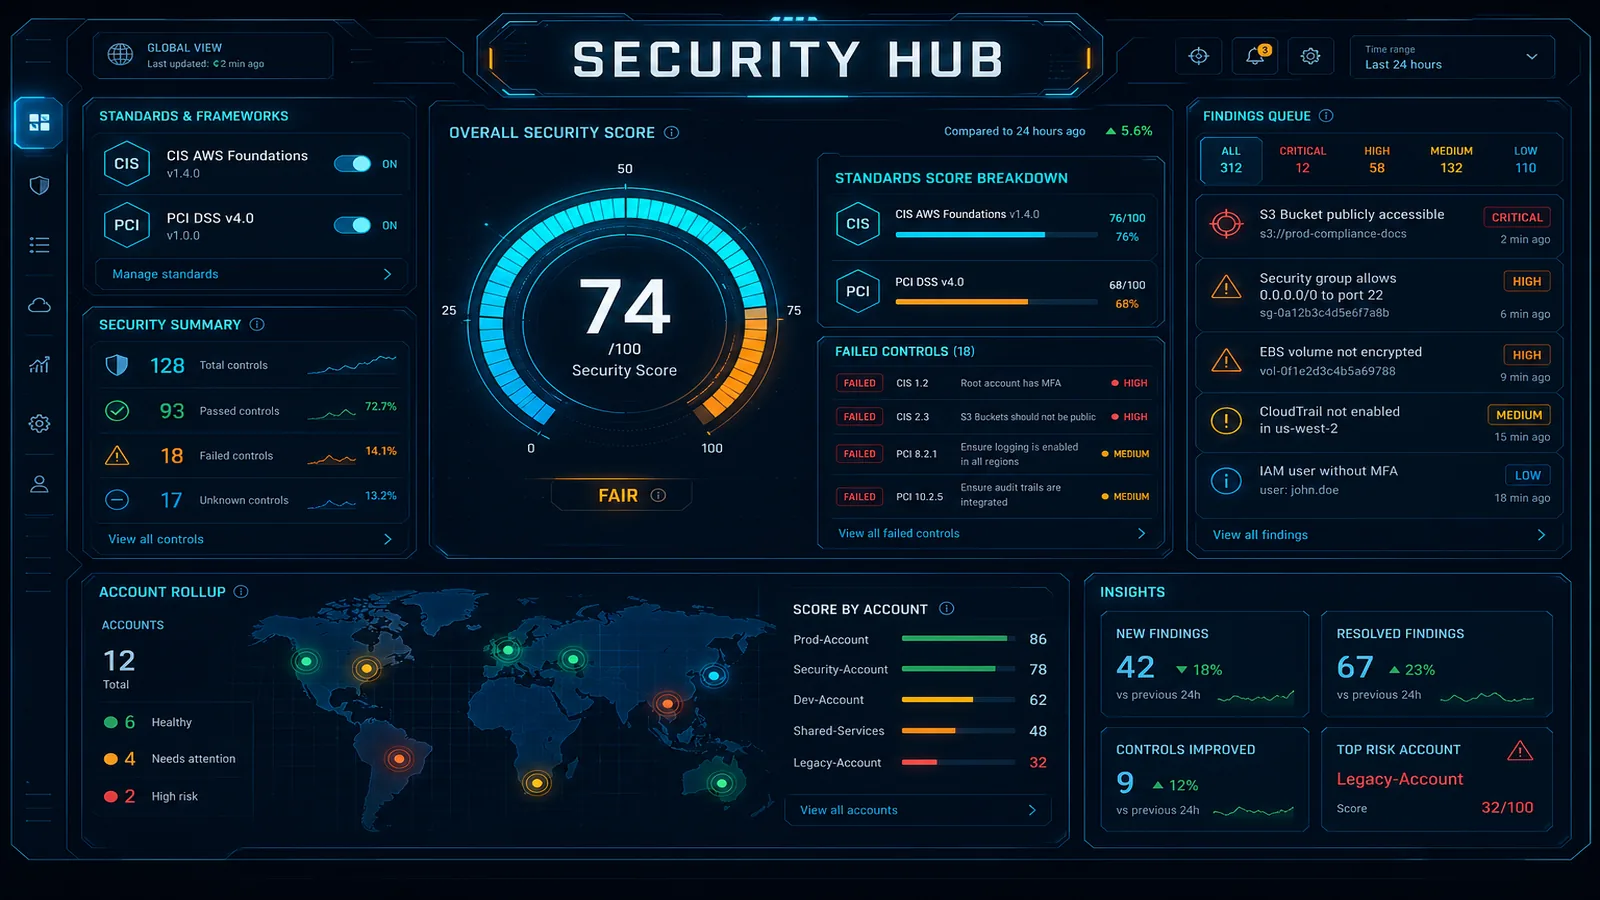
Nash OgdenAWS Security Hub aggregates security findings from 200+ sources and, as of Jul 14 2026, includes AI inventory for org-wide AI assets. As of 6 Nov 2026 it also includes an SBOM inventory of packages on EC2, ECR, and Lambda. This guide covers setup, compliance standards, both inventories, automated remediation, and a compliance dashboard without hiring a SOC team.
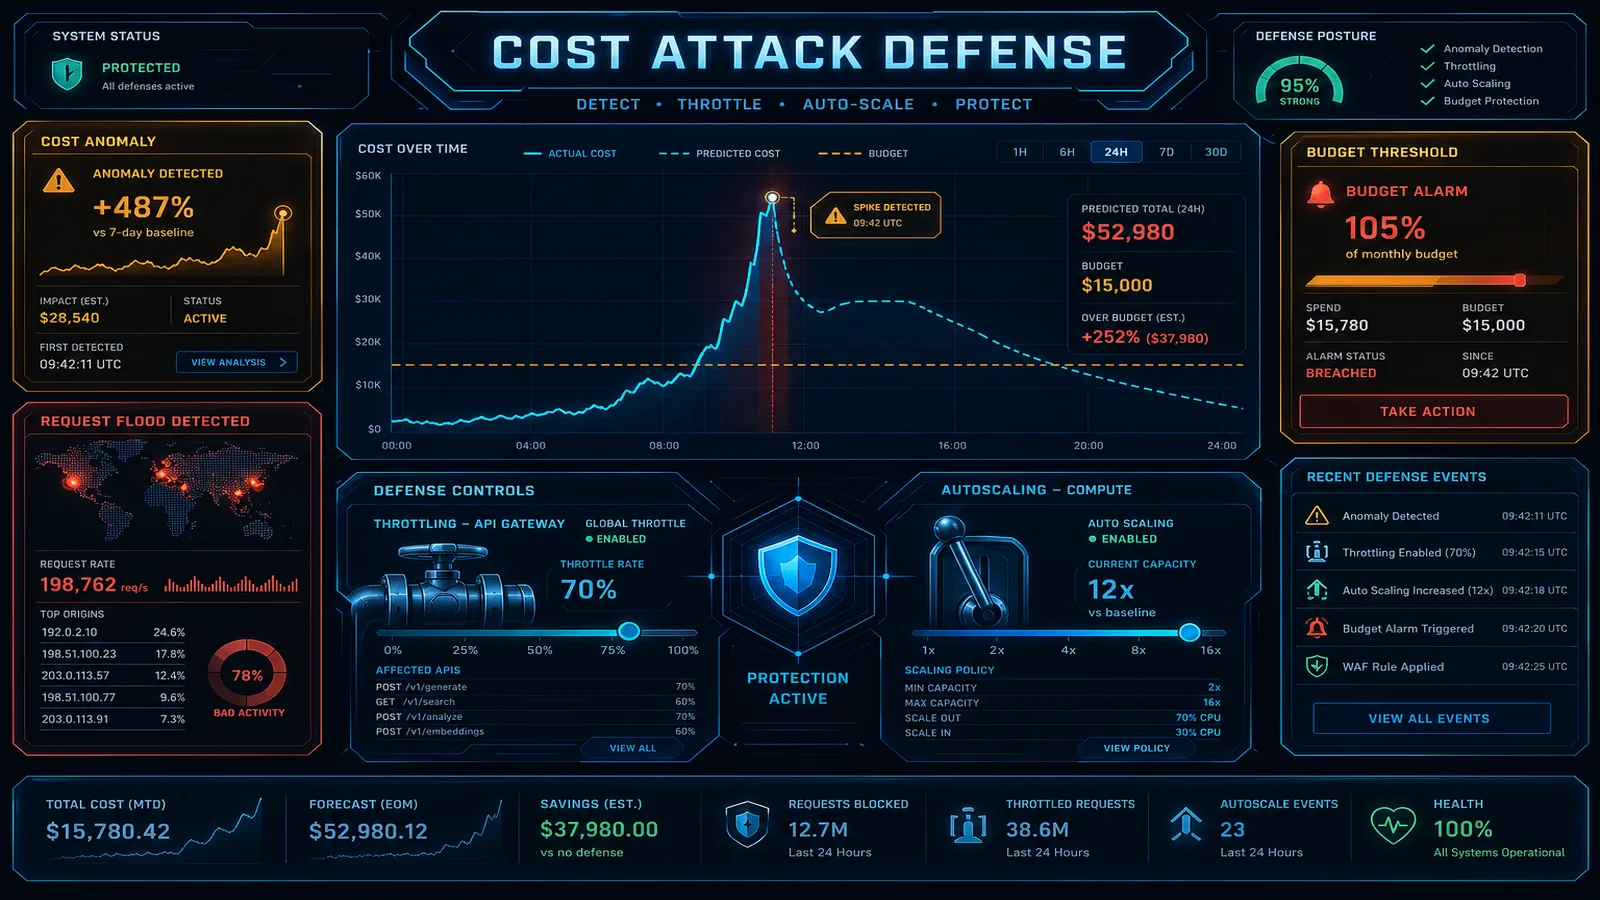
Nash OgdenBilling attacks: CloudFront request floods, Lambda bombs, SQS/SNS OTP spam. July 2026: WAF ceilings, reserved concurrency, Budgets Actions, FinOps backstops.
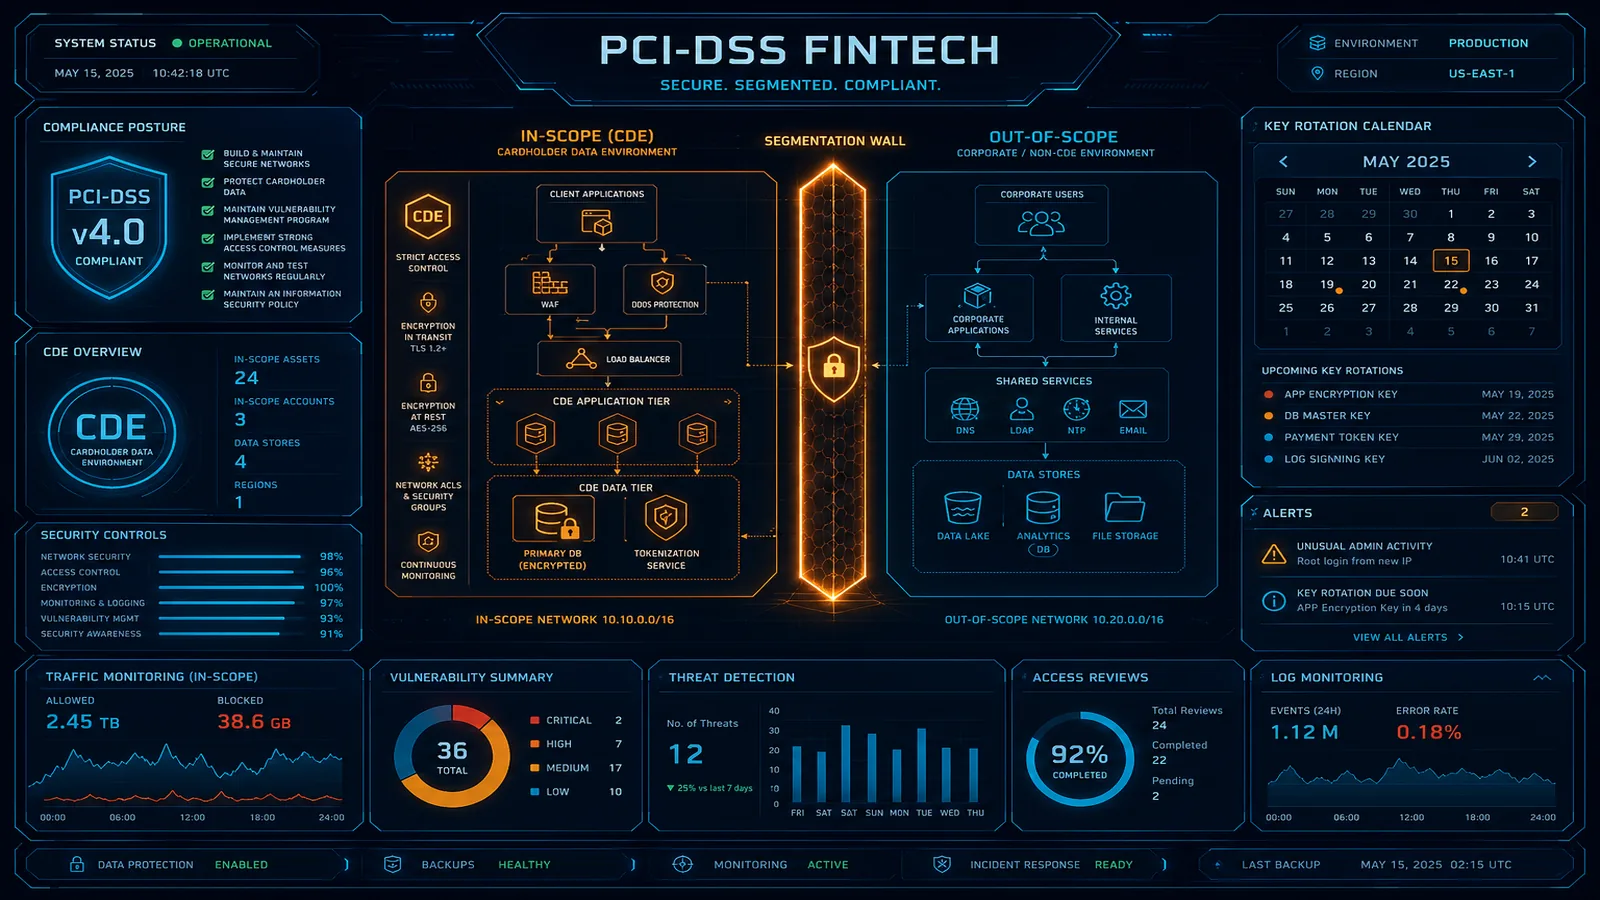
Nash OgdenA practical architecture guide for PCI DSS compliance on AWS: CDE scoping, the 12 requirements mapped to AWS services, network design, encryption, logging, and audit readiness for payment-processing applications.
Nash OgdenManual security triage cannot keep up with cloud-scale threats. This post wires GuardDuty Extended Threat Detection, Security Hub, EventBridge, and Lambda into a self-healing AWS security architecture.
Nash OgdenLeast privilege is easy to say and harder to run at production scale. This covers roles vs users, permission boundaries, SCPs, identity federation, and the access-control patterns that keep teams fast without leaving keys lying around.
Nash OgdenSecrets Manager rotates and costs $0.40 per secret per month. Parameter Store doesn't rotate and is mostly free. Pricing, rotation, encryption, cross-account access, and the decision criteria for picking each, including the hybrid pattern most production accounts end up at.
Nash OgdenAWS WAF blocks attacks. It also blocks legitimate users when the rules are wrong, which is a worse incident. Managed rule groups, custom rules, rate limiting, bot control, and the layered defense strategy that protects without flooding your support queue.
Nash Ogden