Patch the 2026 developer stack in this order
A working list of 27 dates, from 26 January through 3 November 2026, covers Django, Next.js, PHP, Node.js, Docker, nginx, and npm. Axios 1.14.1 and 0.30.4 were malware for about 3 hours on 31 March.
Blog category
Practical AWS security guides covering IAM least-privilege, GuardDuty, WAF, Secrets Manager, VPC design, and compliance automation. Built from real remediation work across SOC 2, HIPAA, and PCI-regulated environments.

A working list of 27 dates, from 26 January through 3 November 2026, covers Django, Next.js, PHP, Node.js, Docker, nginx, and npm. Axios 1.14.1 and 0.30.4 were malware for about 3 hours on 31 March.


A 280-user SaaS ops team cut Client VPN connection-hours ~62% after moving 34 HTTPS apps to Verified Access. Site-to-Site on TGW stayed for the colo; full-tunnel Client VPN had been burning ~$1.1k/mo in idle connection fees.
After the April 2026 S3 default that blocks SSE-C on new buckets (and on existing buckets in accounts with zero SSE-C objects), a SaaS media platform (~2.4 PB, 418 buckets) found 11 legacy upload paths still sending customer-key headers, all failing with 403 until migrated to SSE-KMS.
Shield Advanced is $3,000/mo per org plus DTO fees. For a consumer marketplace (~180M req/mo CloudFront), cost protection credited $41k in scaling charges after a 38-minute L7 event when WAF rate rules were pre-configured.
On a defense-subcontract SaaS (~$42k/mo AWS, CUI in scope), choosing GovCloud (US) over commercial US-East cut inherited-control review from 11 weeks to 4 after mapping 47 customer-responsibility controls in the SSP inheritance worksheet.
Most remote-access RFPs still default to full Windows desktops, but 60%+ of contractor work is browser-only. WorkSpaces Secure Browser isolates SaaS in AWS; WorkSpaces Applications (formerly AppStream 2.0) streams fat clients without a desktop. A composite regulated services firm cut 3 legacy VDI vendors to 2 OU-scoped patterns and reduced unmanaged-endpoint incidents from ~9/quarter to ~2 after splitting browser vs app streaming.
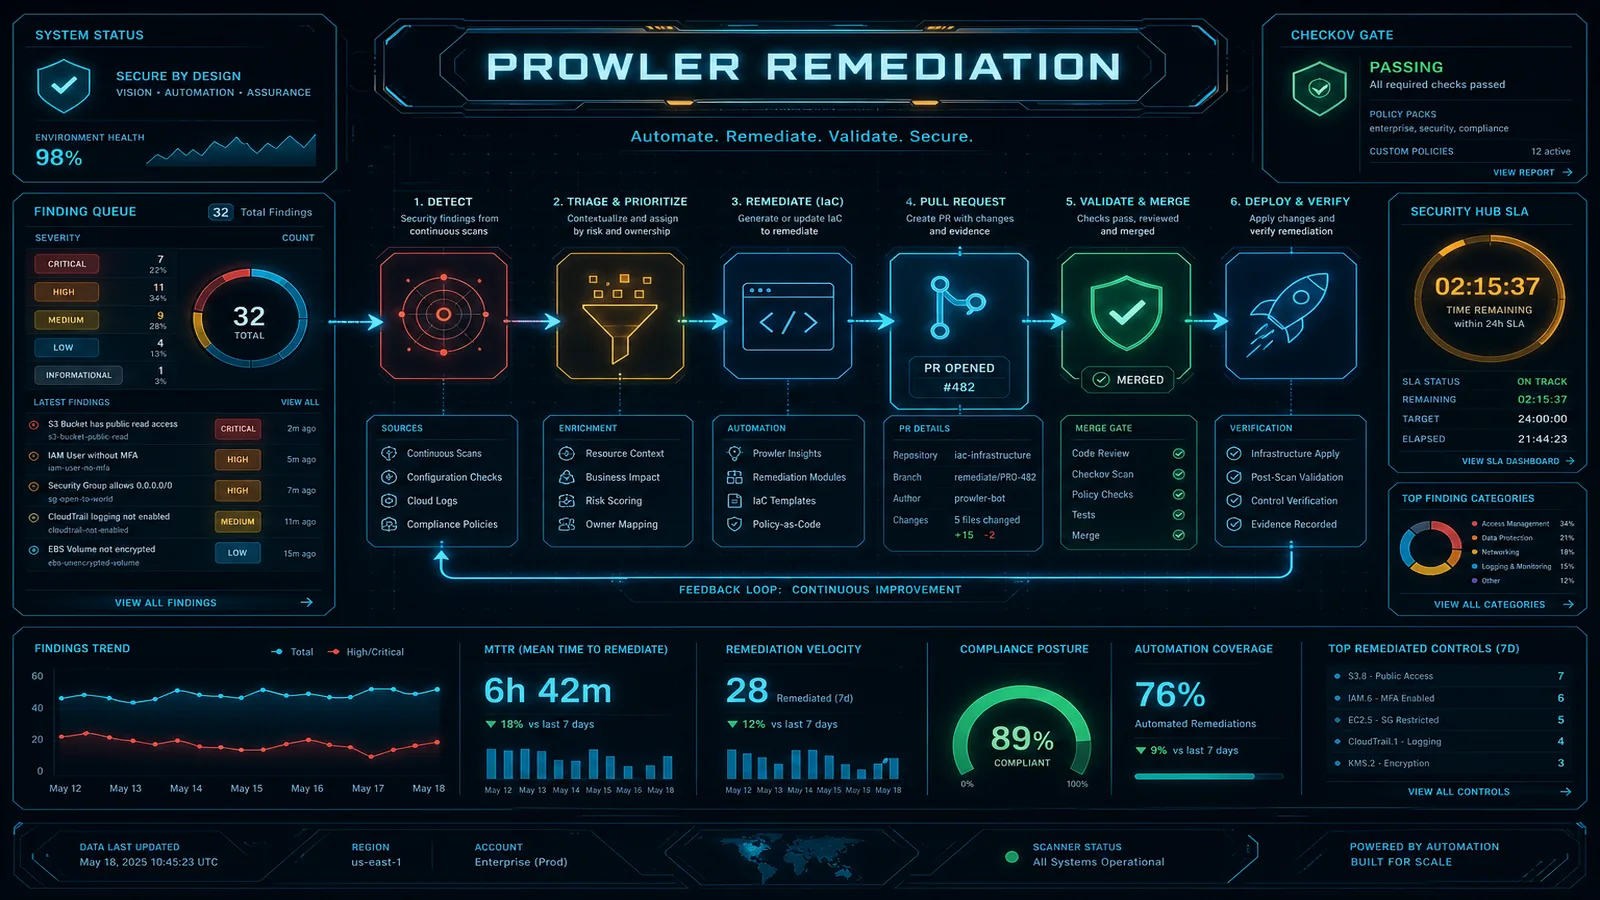
Prowler finds AWS misconfigurations. This guide covers who remediates findings, IaC fix patterns, Security Hub workflows, and when to bring in AWS security consulting.
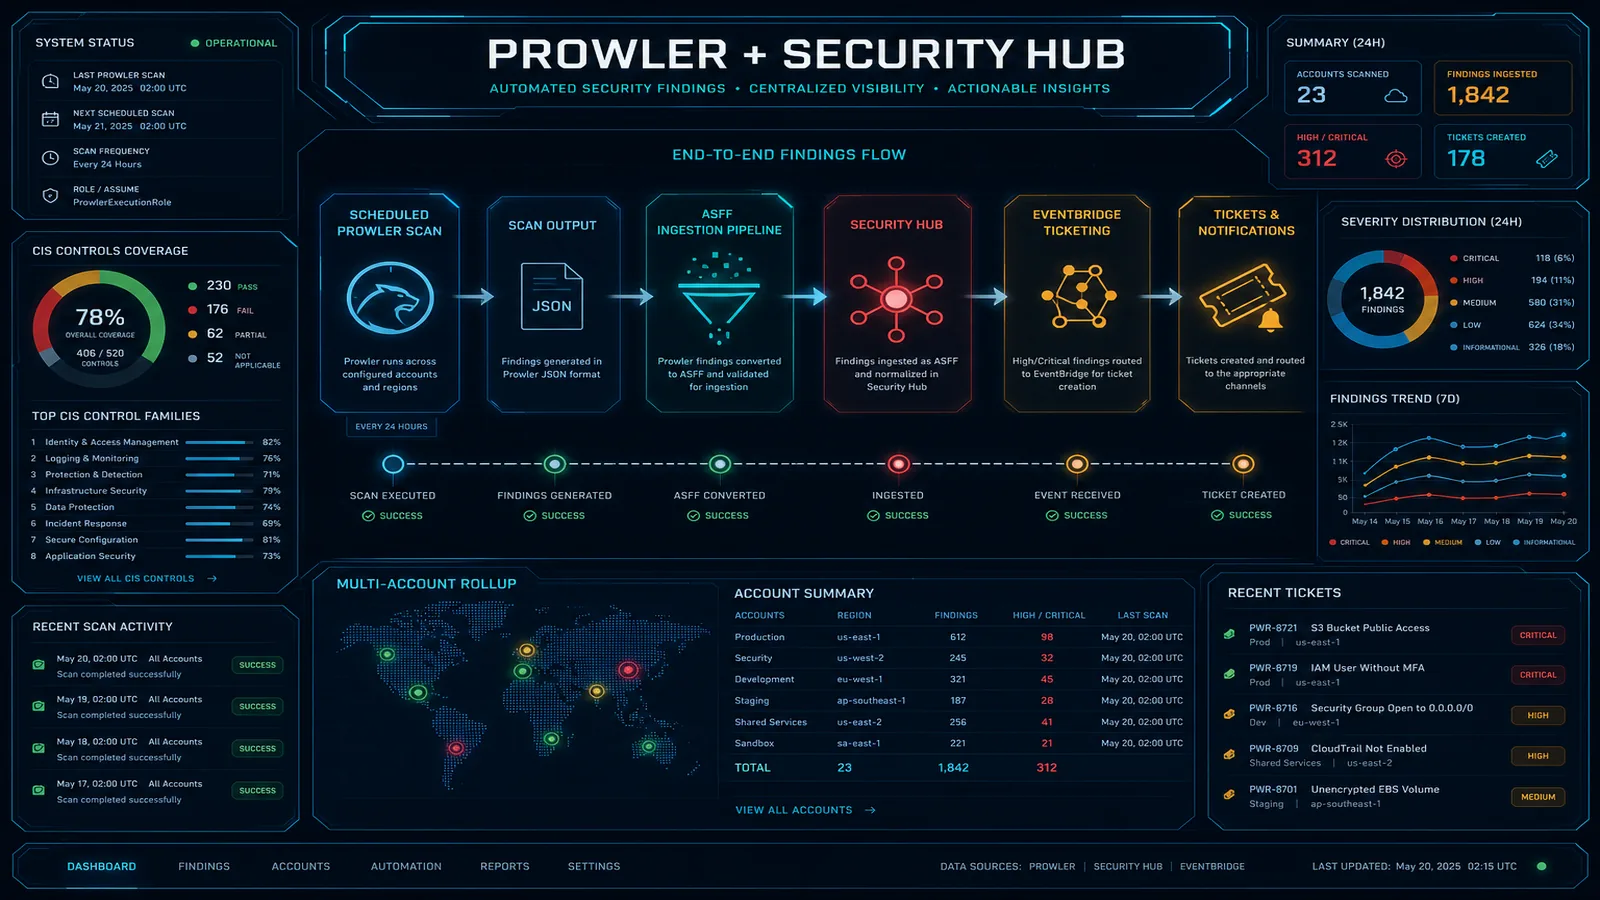
Production checklist for Prowler and AWS Security Hub: multi-account setup, scheduled scans, finding workflows, and remediation patterns on AWS.
We use cookies and similar technologies to analyze site traffic, personalize content, and provide social media features. By clicking “Accept,” you consent to our use of cookies. You can adjust your preferences at any time.